This gallery includes all fourteen screenshots stored in the preserved GCP validation collection. The images are delivered by this website and can be opened at their full original dimensions. Each card identifies the expected and recorded observation, its source, any privacy redaction, and what the capture cannot establish. The collection README attributes the captures to 23 August 2026; that is an owner-recorded collection date rather than a new independently authenticated execution timestamp.
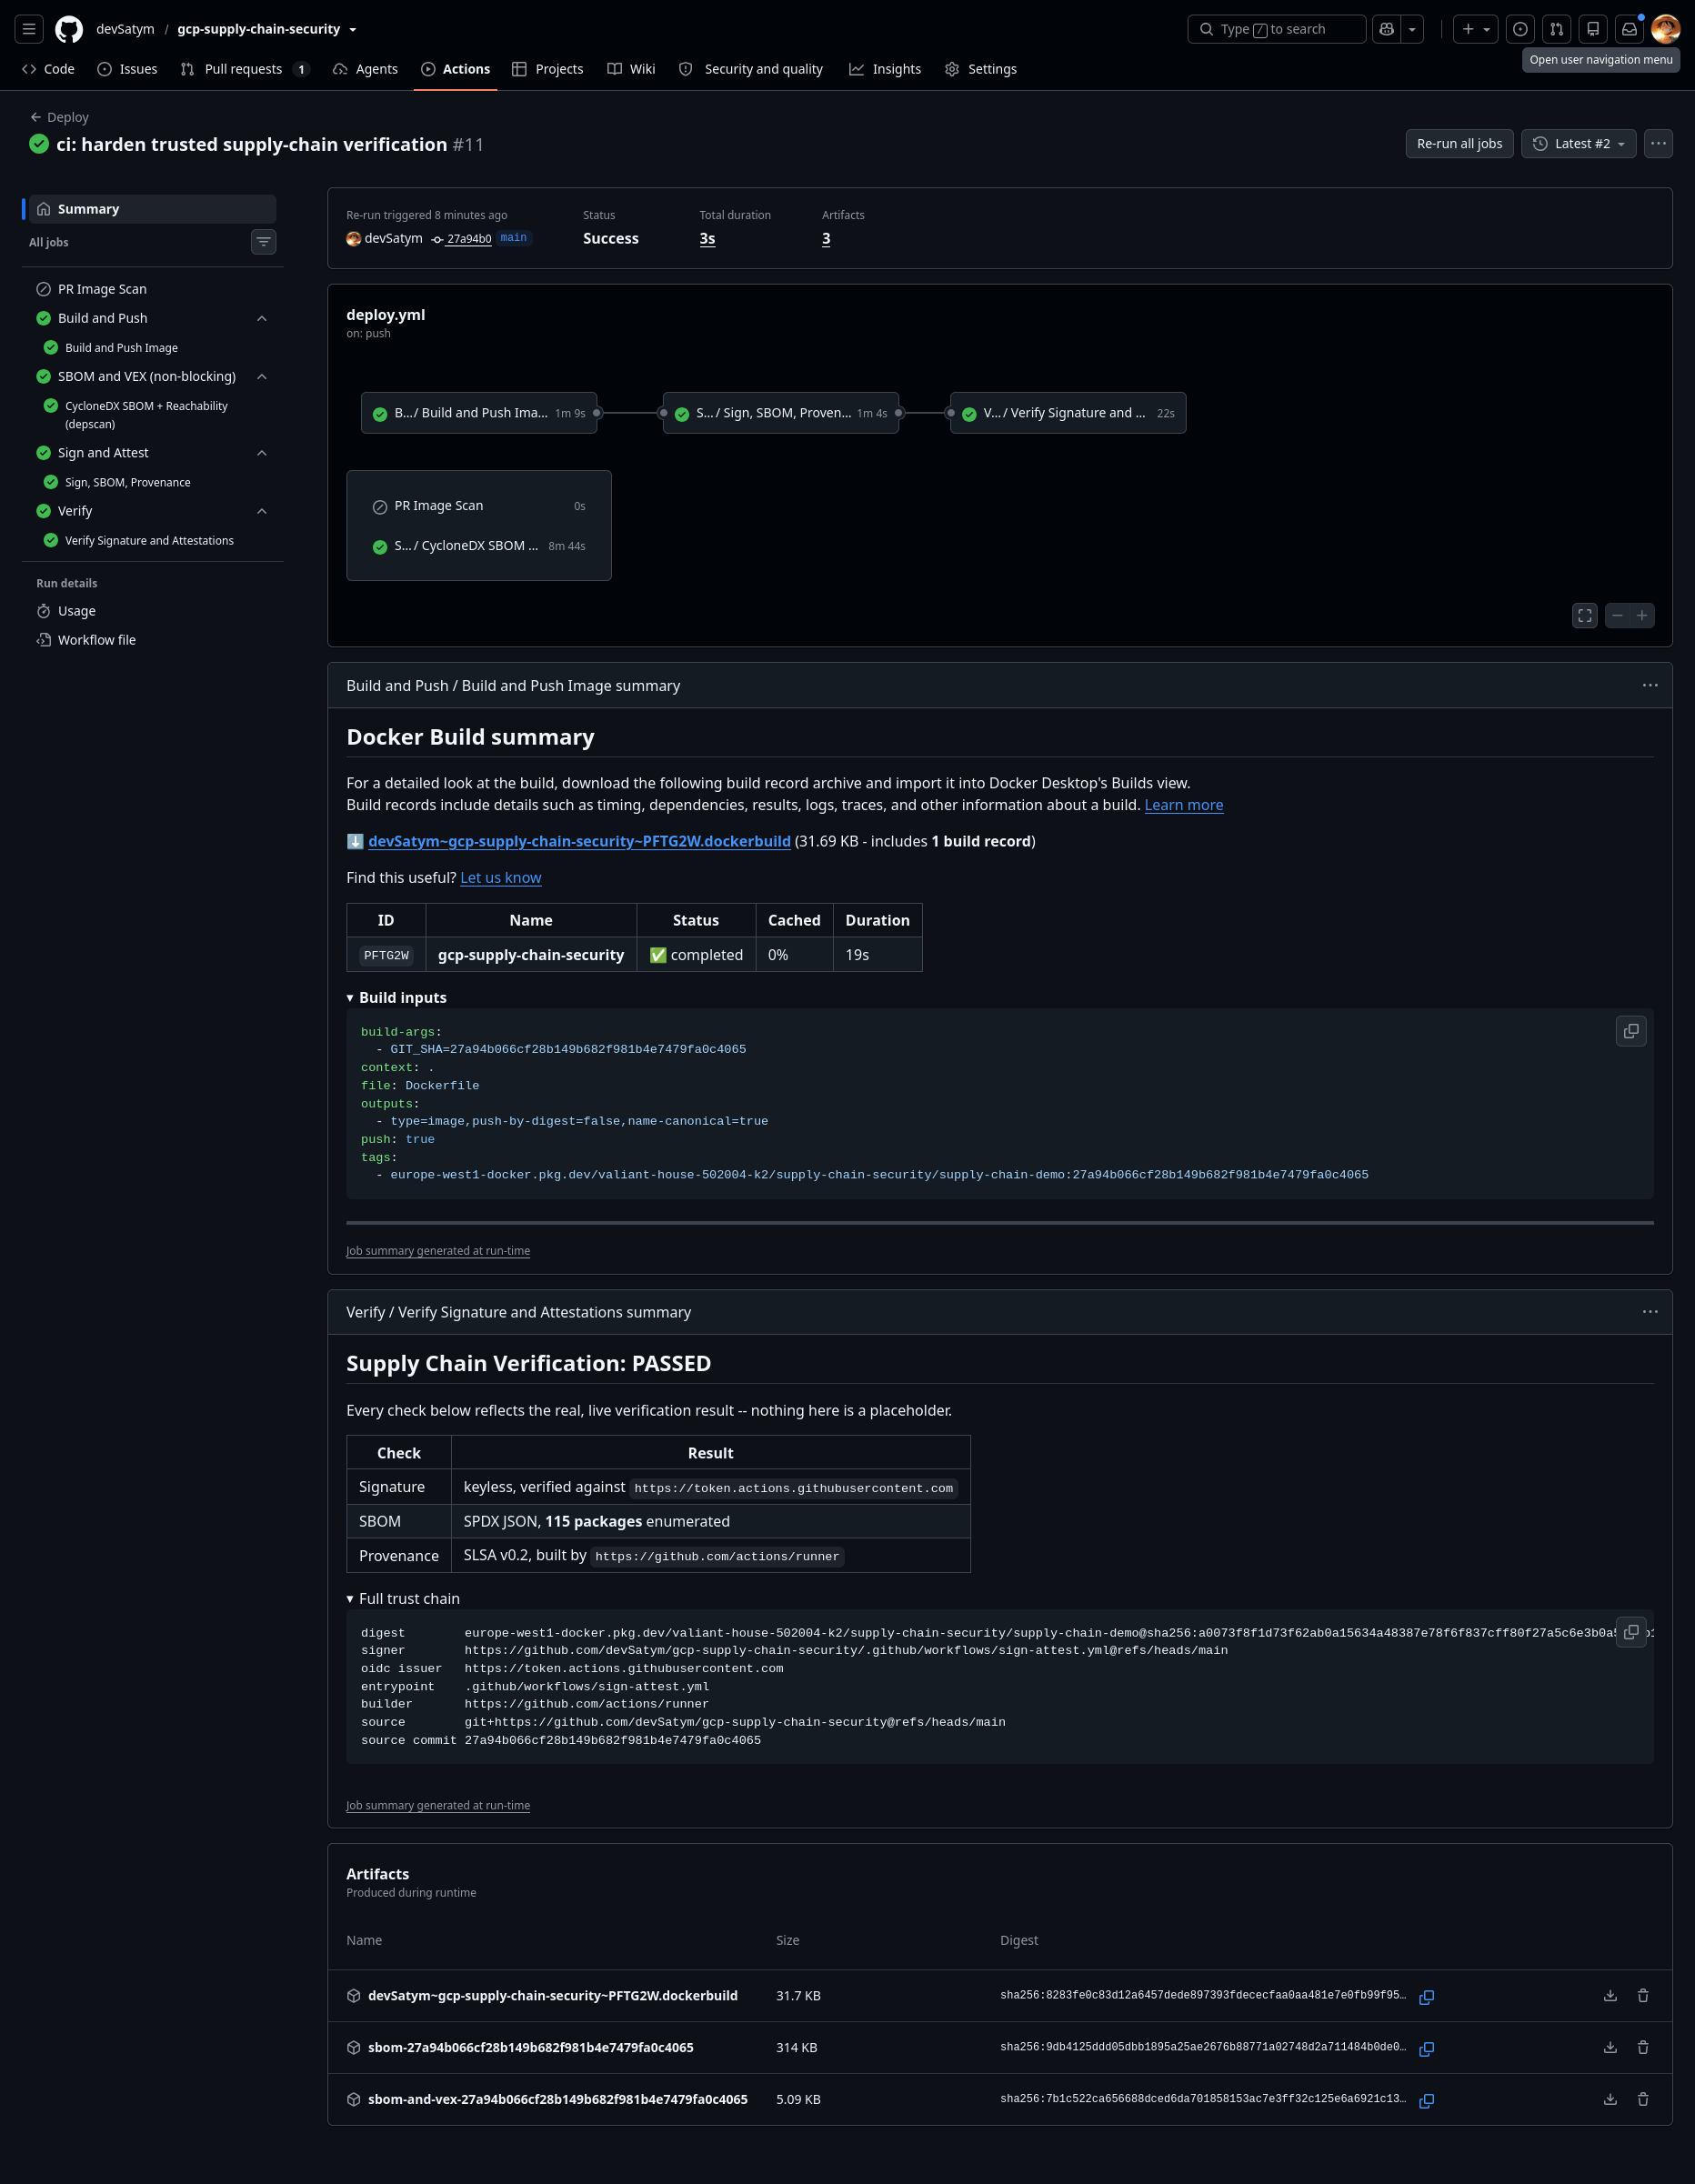
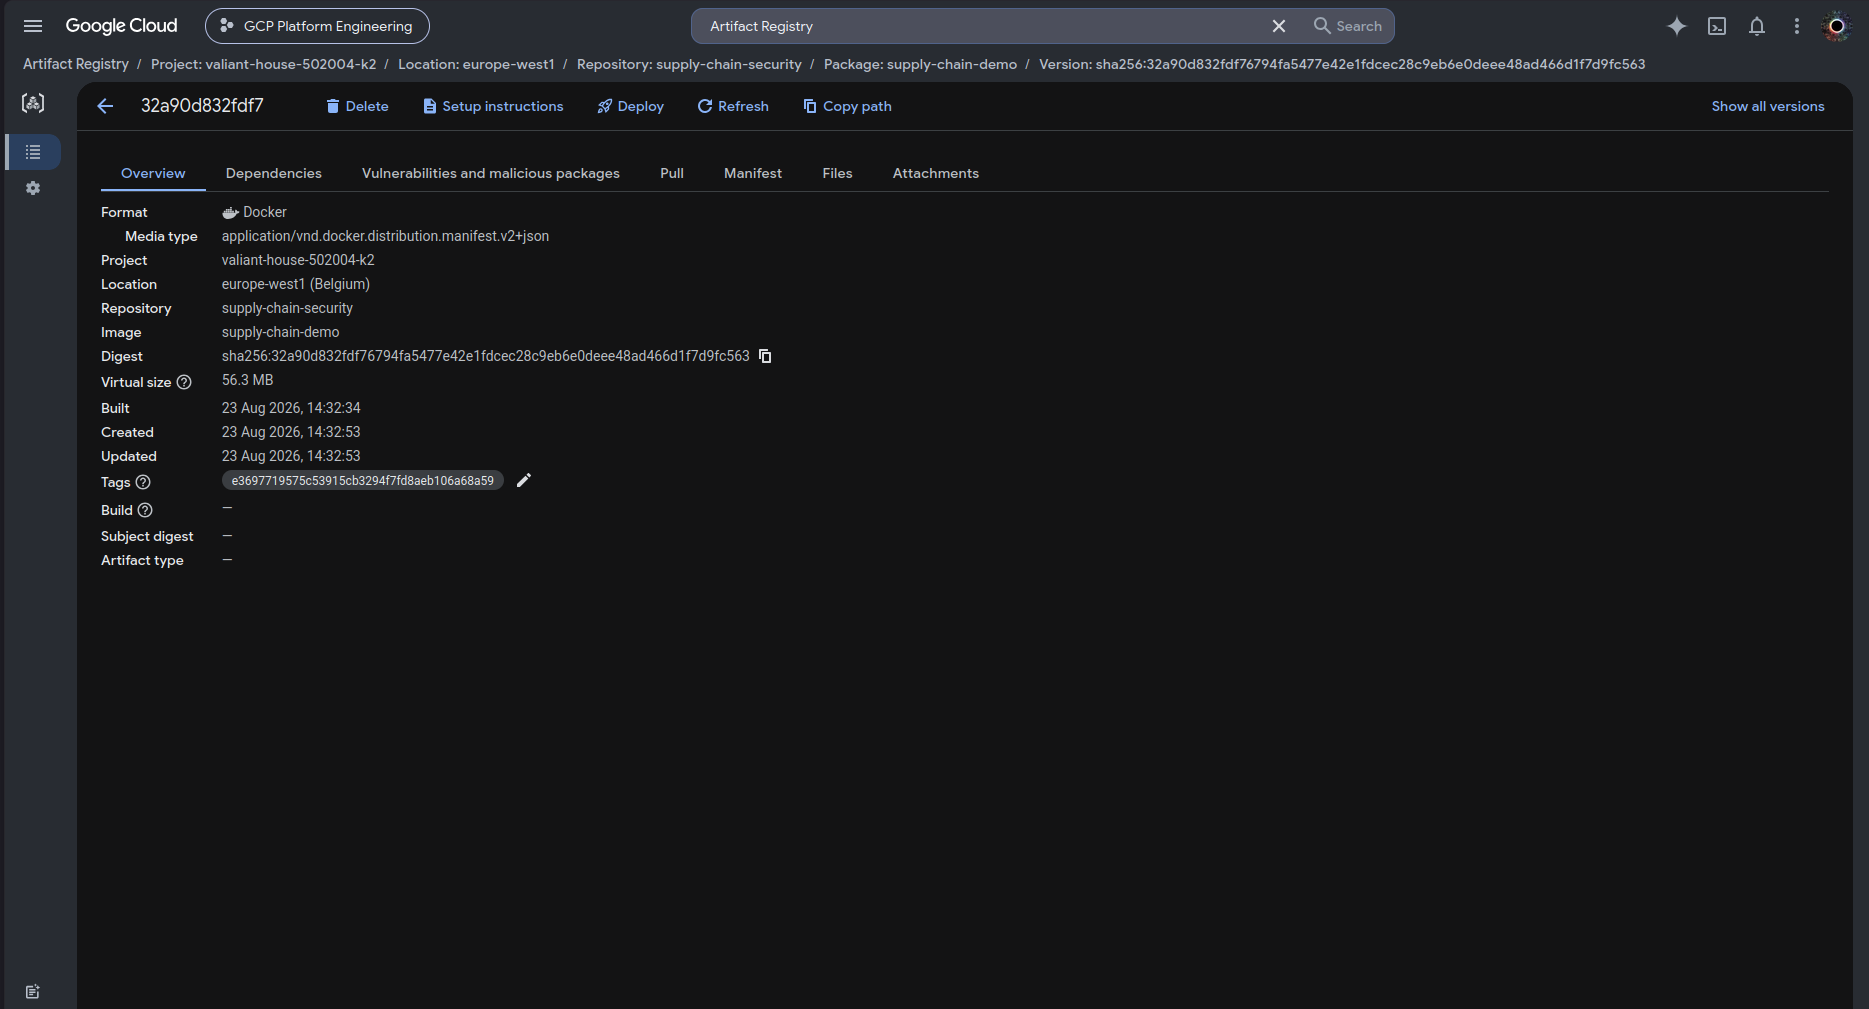
These captures do not form a single verified release trace. The CI and attestation images show source 27a94b0 and an artifact beginning a0073f8f; the registry, Deployment specification, and trusted dry-run concern 32a90d…. Argo sync revisions are separate GitOps fields. A screenshot of a configured Deployment digest does not establish the running container’s imageID, and readiness does not prove cryptographic enforcement.
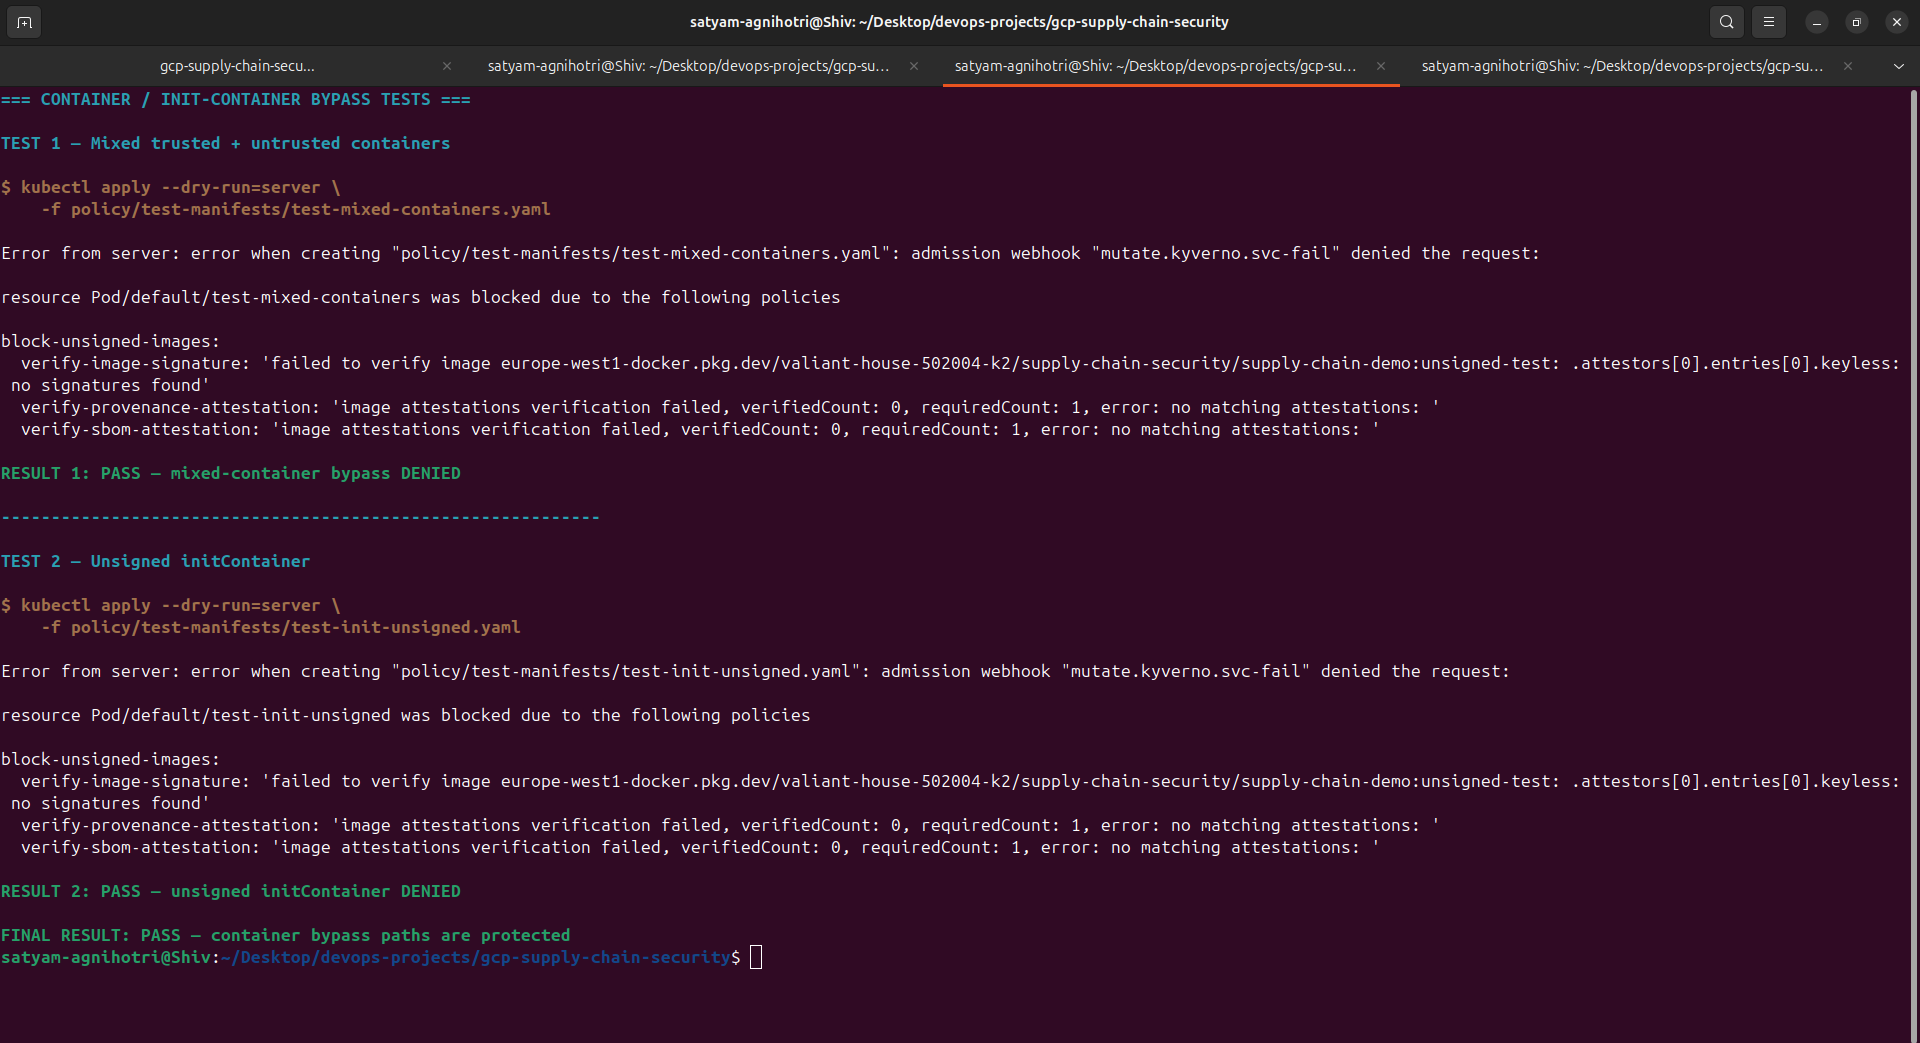
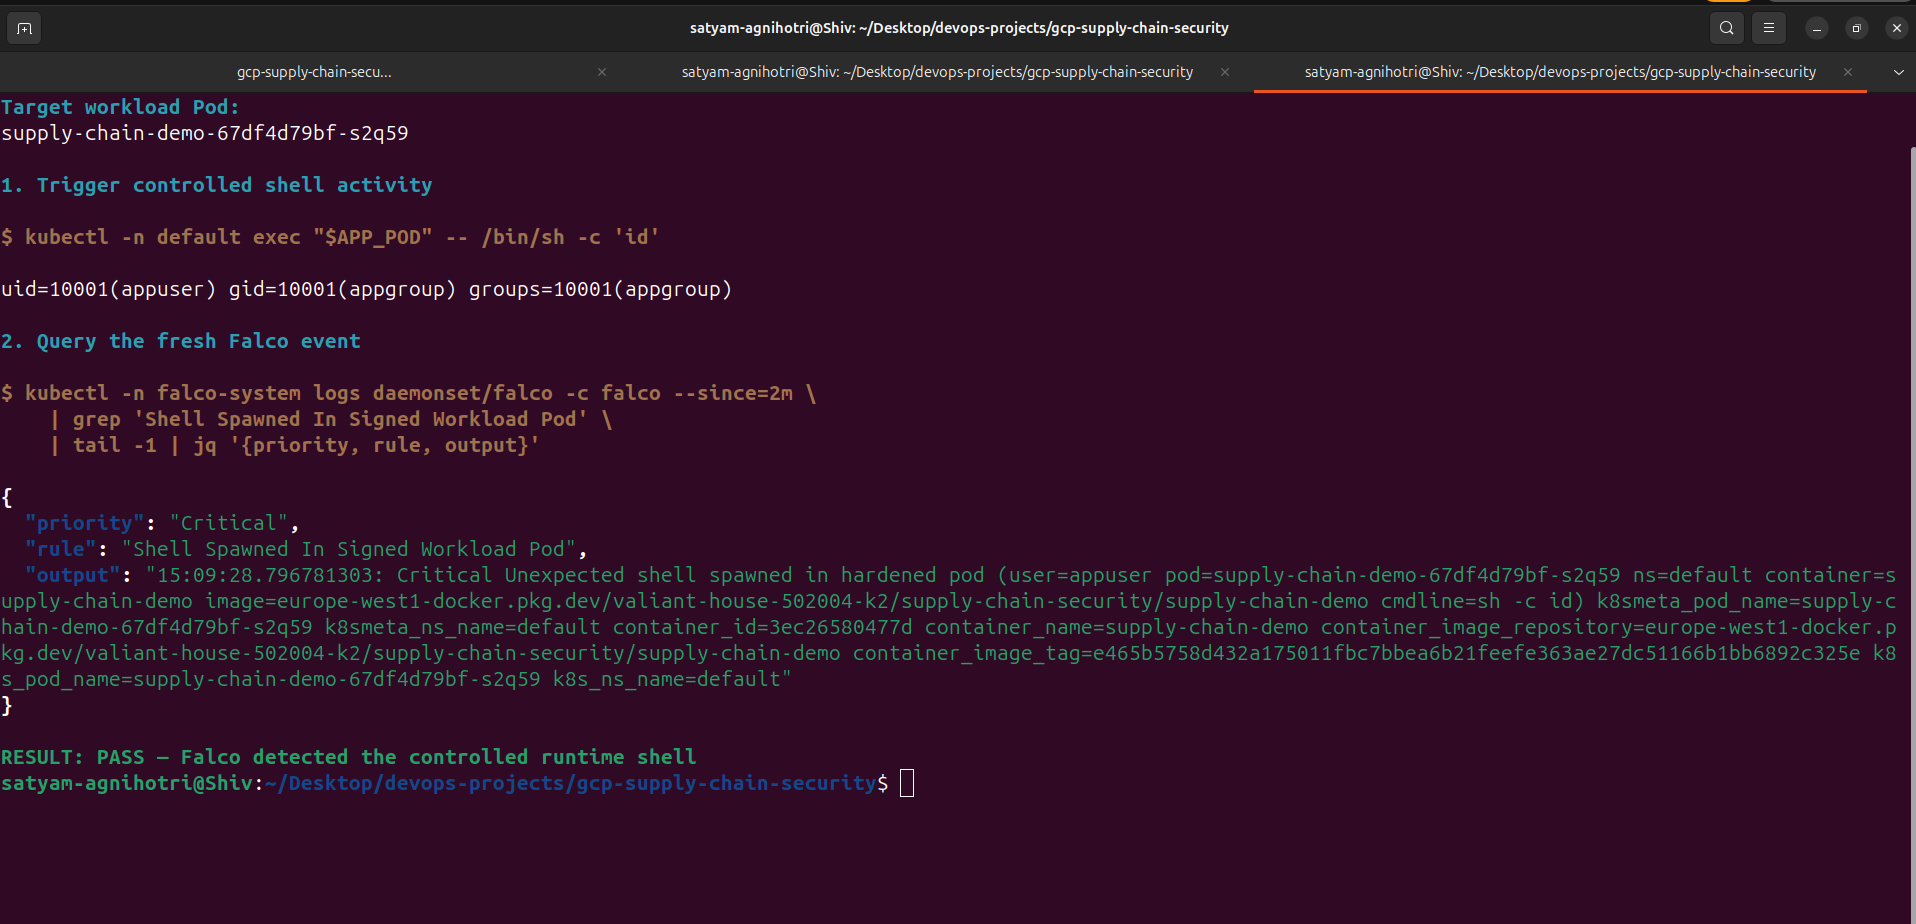
The PR capture shows an open proposal with passing checks. The denial cases demonstrate their recorded scoped experiments. Wrong-trust changes two expectations together, and both mixed-image fixtures use an unsigned initContainer. Falco records detection after the controlled shell executes. These images provide historical observations, not current cloud health or freshly executed tests.
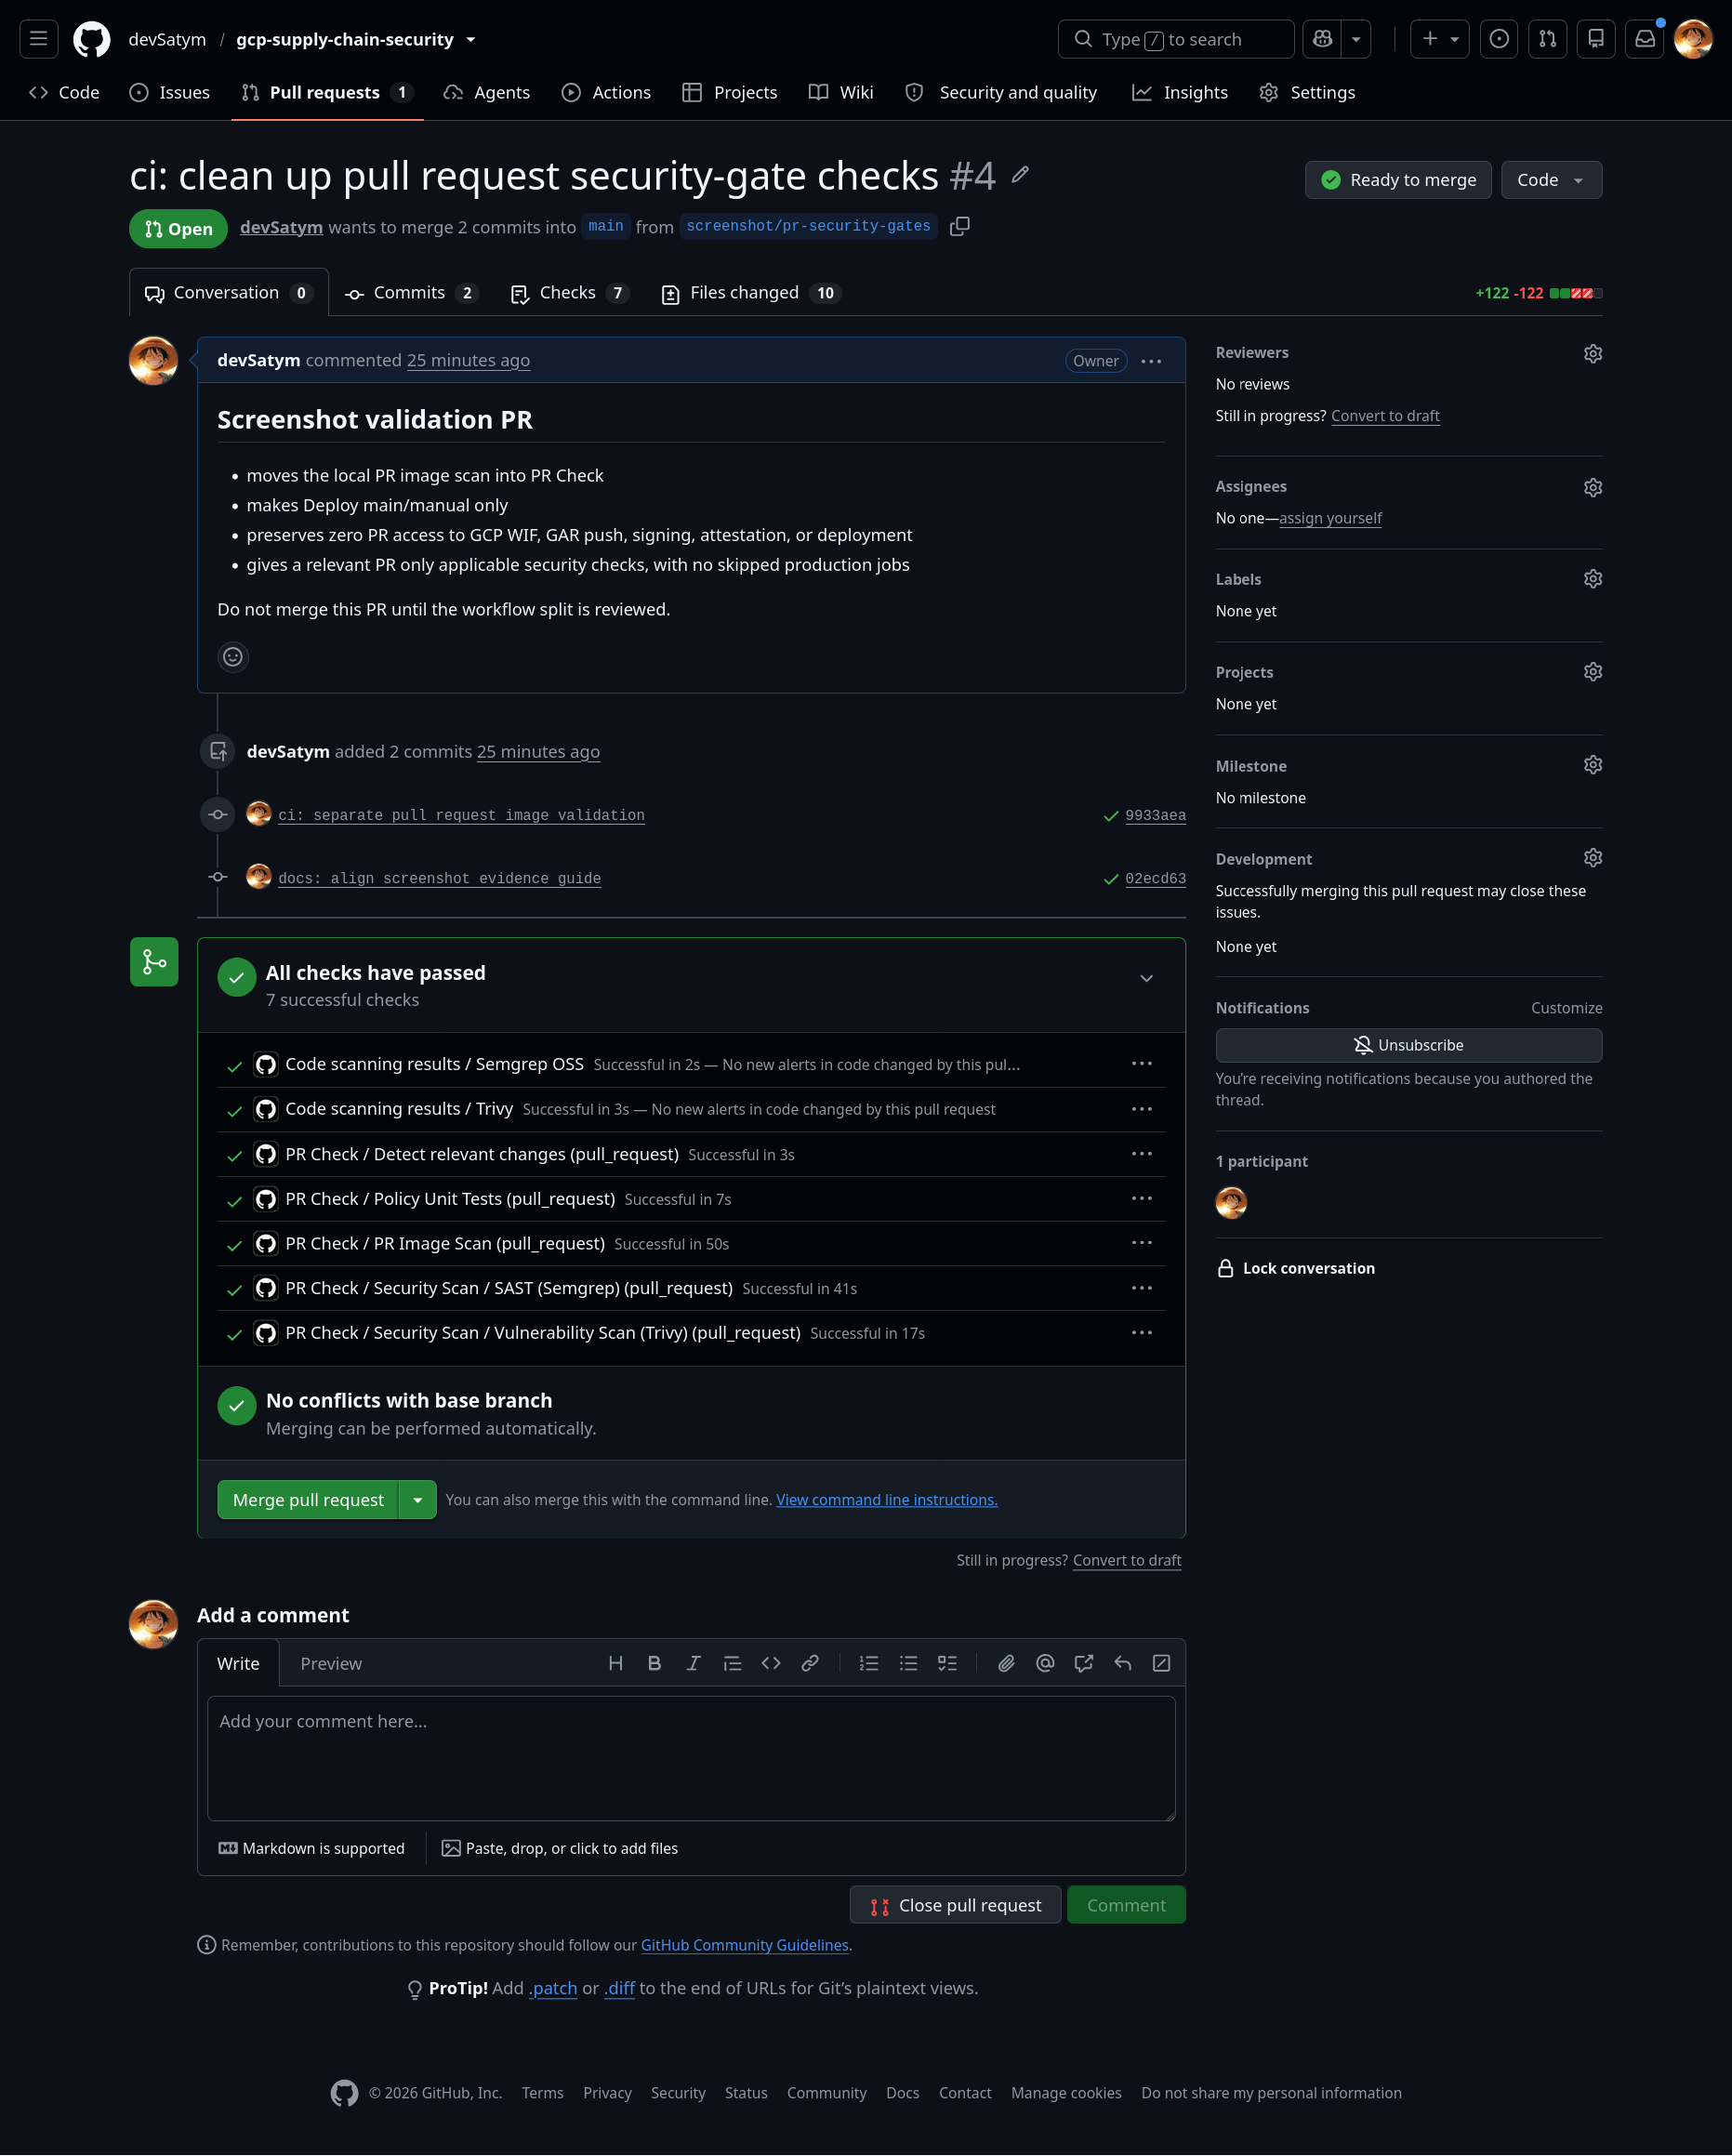
Seven checks are displayed as successful on an open pull request. Select the image to read the complete capture at full resolution.
Expected: All proposed PR checks complete successfully. Recorded: Seven green checks are visible; the pull request remains open.
Collection date: (owner README). Open PR proposal; no execution revision is borrowed from later screenshots.
What this does not establish: The proposal asks for review before merging and moves PR Image Scan into PR Check; it does not establish merge approval or the pinned baseline workflow split.
Provenance and privacy review
Original capture reviewed and displayed unchanged. Any blacked-out source regions were already present in the original; this website added no edits. Review: .
What this does not establish: The visible source is 27a94b0 and artifact begins a0073f8f; this is distinct from the live-admission artifact.
Provenance and privacy review
Original capture reviewed and displayed unchanged. Any blacked-out source regions were already present in the original; this website added no edits. Review: .
What this does not establish: Registry presence and a tag do not authenticate provenance, prove deployment or establish current registry state.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
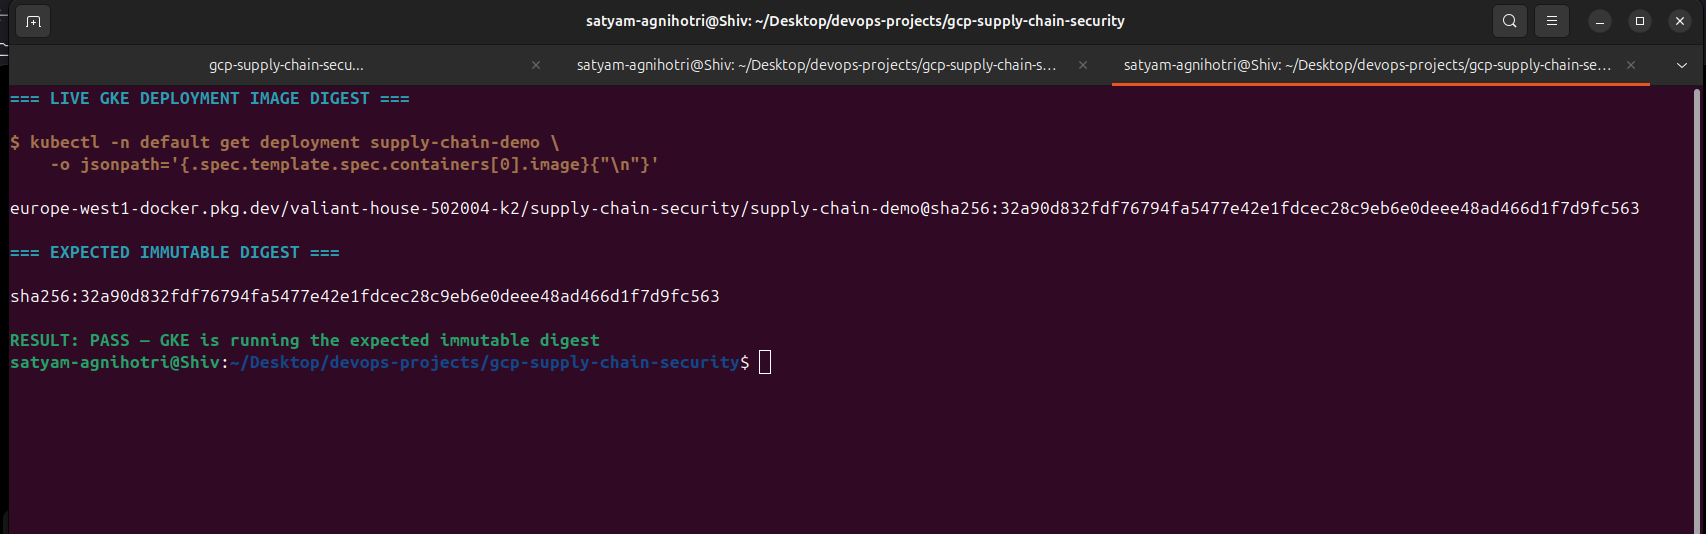
The queried Deployment image specification matches the expected digest beginning 32a90d. Select the image to read the complete capture at full resolution.
Expected: The Deployment specification selects the reviewed digest. Recorded: Expected and queried image strings match.
Collection date: (owner README). 32a90d artifact family; workload build revision is not inferred.
What this does not establish: This queries the Deployment template, not the running container imageID. It cannot establish current workload identity.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
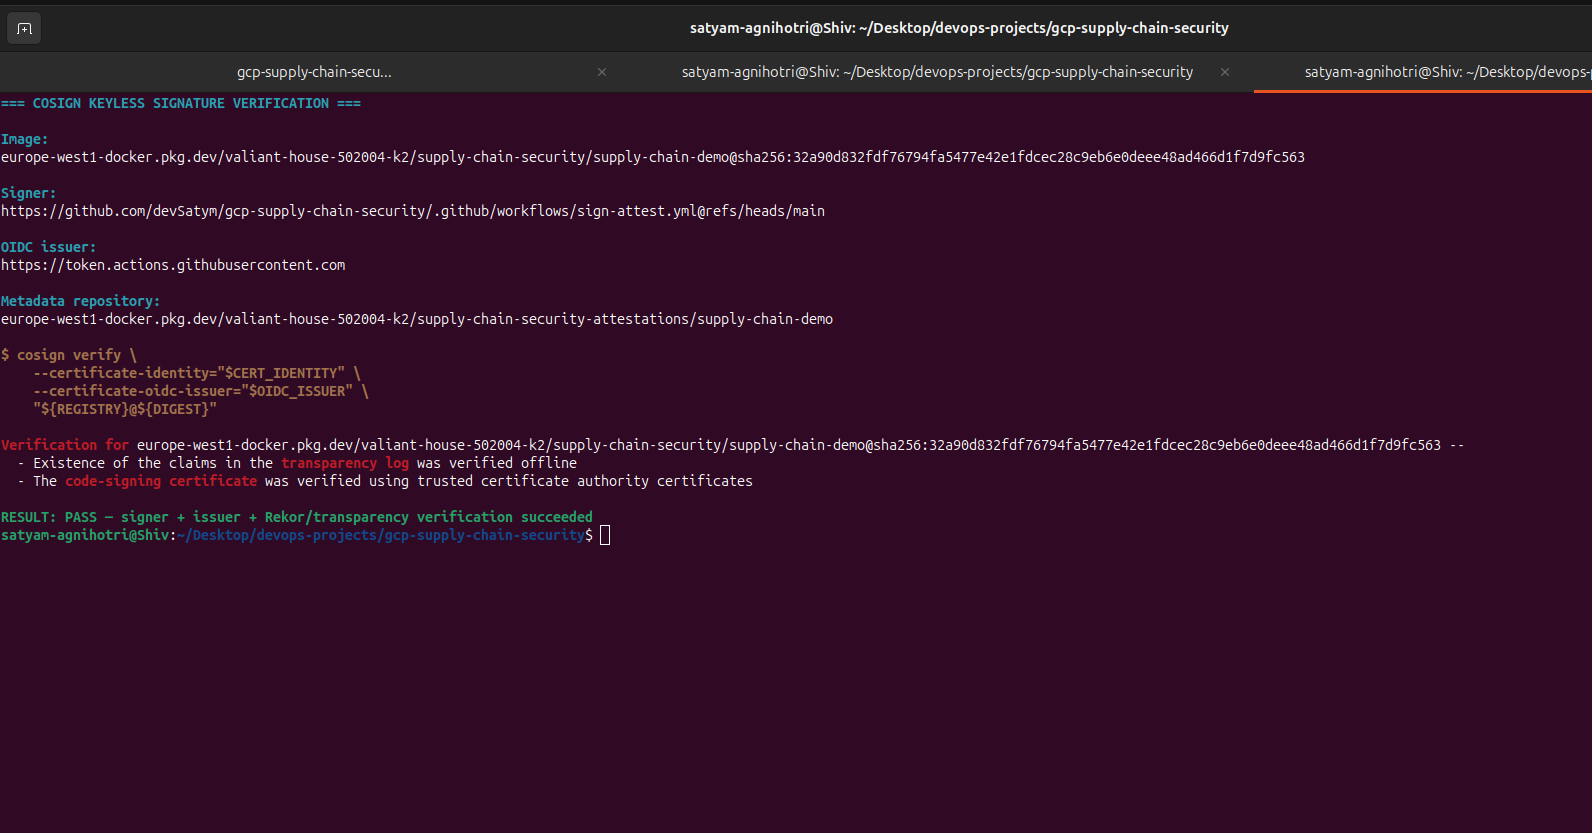
Cosign output records the canonical signer, issuer and transparency verification for the selected artifact. Select the image to read the complete capture at full resolution.
Expected: Cosign accepts the expected keyless certificate identity and issuer. Recorded: Signature verification succeeded for the pictured 32a90d artifact.
Collection date: (owner README). 32a90d artifact family; independent of the a0073f8f CI screenshots.
What this does not establish: This standalone signature verification does not display SBOM or provenance predicate validation. The browser does not reauthenticate the capture.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
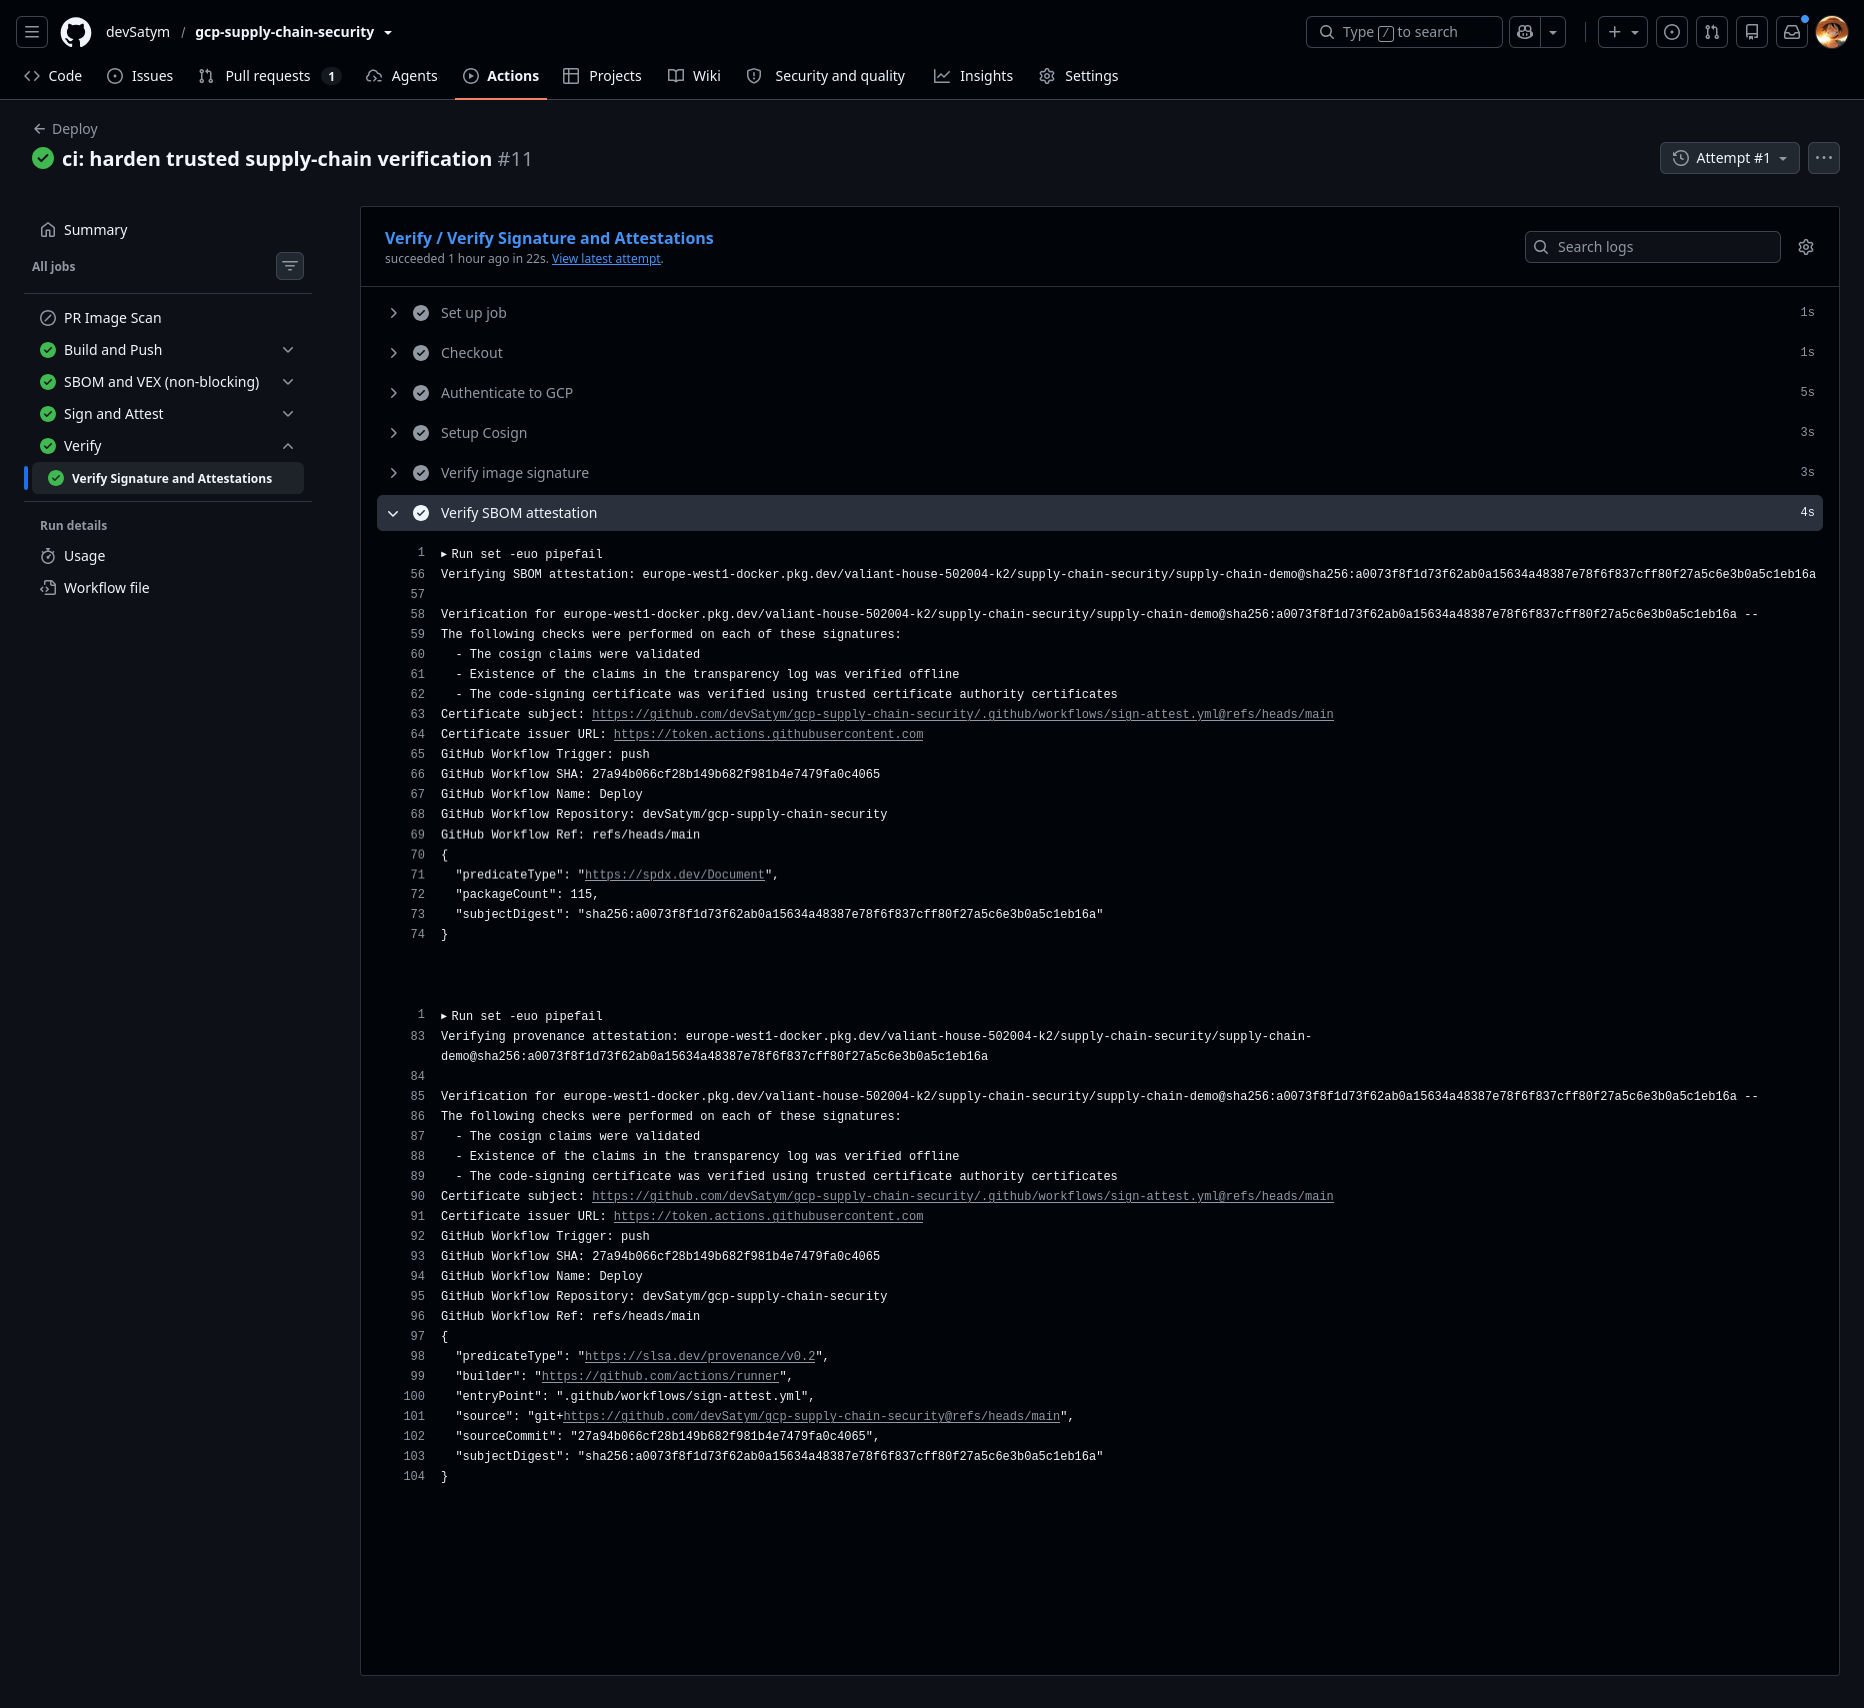
The CI output displays verified SPDX and SLSA v0.2 provenance claims and their inspected fields. Select the image to read the complete capture at full resolution.
Expected: Authenticated claims identify the expected digest, signer, builder and source. Recorded: Verified output reports packageCount 115 and provenance fields.
What this does not establish: 115 packages is not completeness or application safety. A schema version is not a SLSA assurance level. This image shows attempt 1, while the workflow overview shows attempt 2.
Provenance and privacy review
Original capture reviewed and displayed unchanged. Any blacked-out source regions were already present in the original; this website added no edits. Review: .
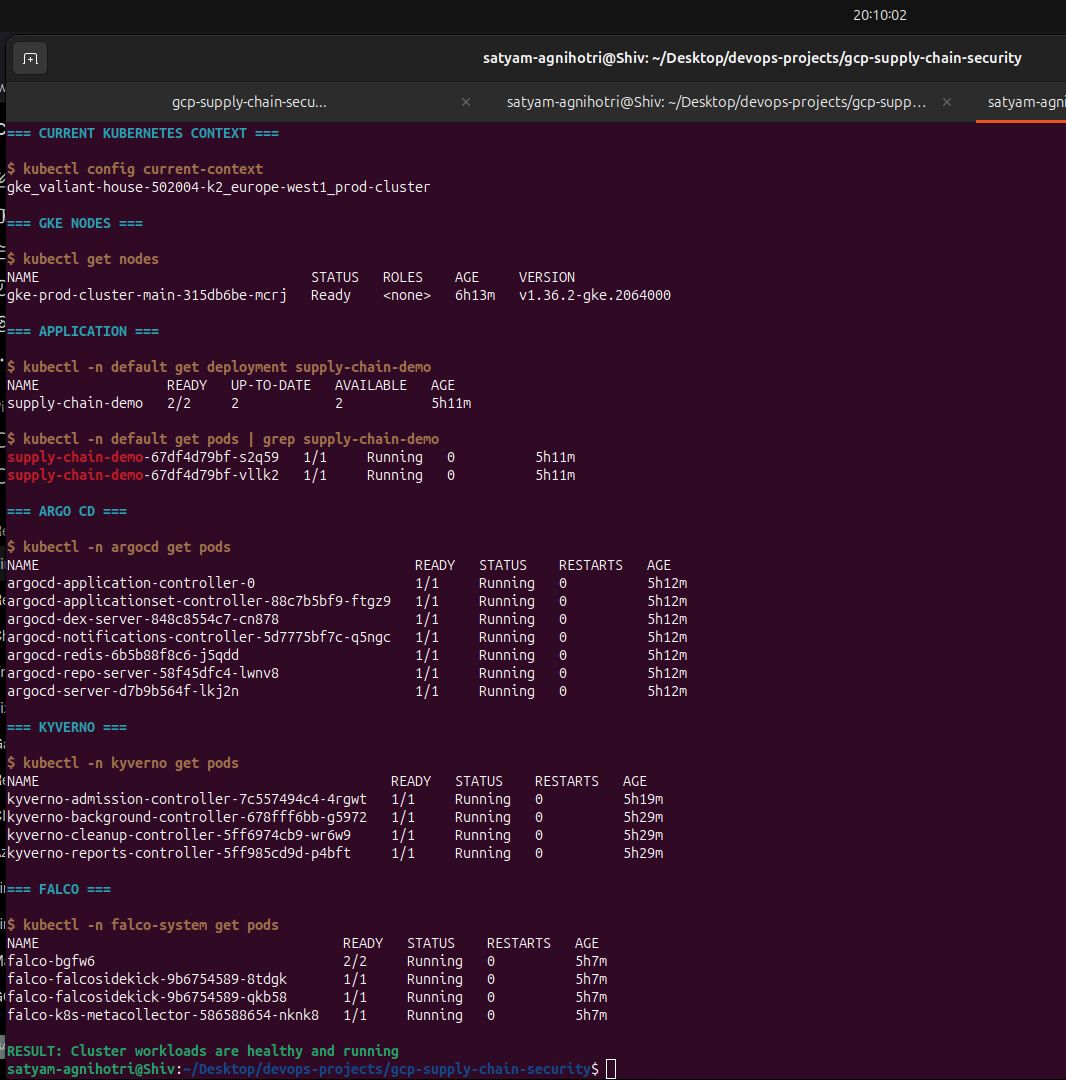
The terminal lists historical node, application, Argo, Kyverno and Falco-related Pod status. Select the image to read the complete capture at full resolution.
Expected: Configured components report ready workload status. Recorded: The captured status queries list their then-current readiness.
Collection date: (owner README). Historical cluster context; no artifact build revision is inferred.
What this does not establish: Ready/Running status does not demonstrate signature enforcement, alert delivery or a currently healthy cluster.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
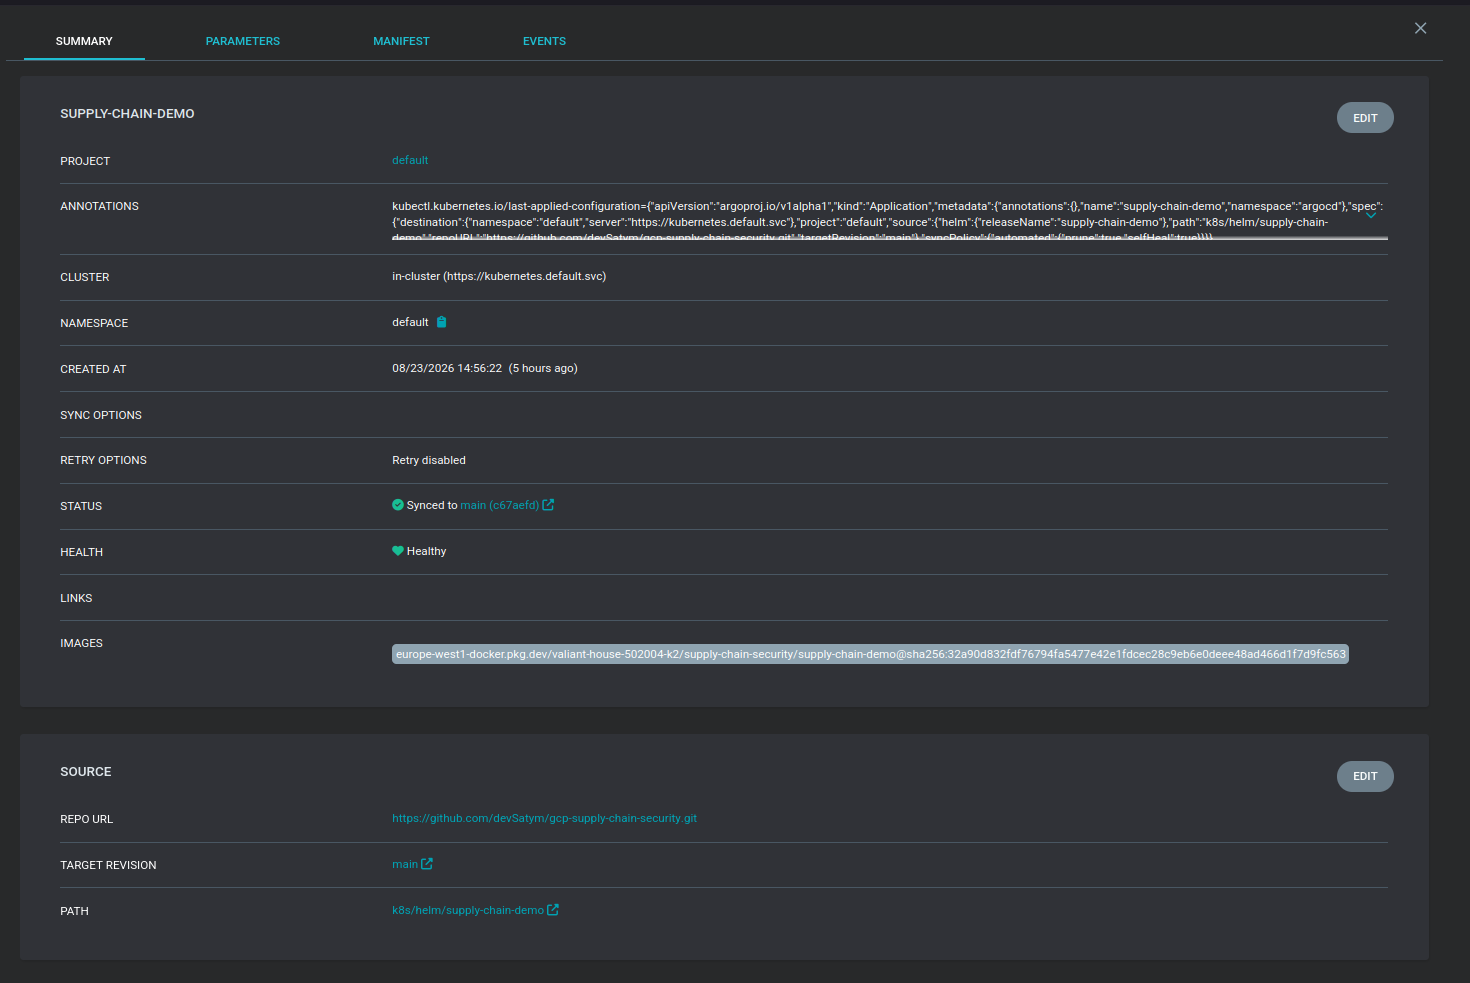
Argo application details show source tracking, Helm path and the selected 32a90d image. Select the image to read the complete capture at full resolution.
Expected: Argo reconciles the selected release and reports the tracked source. Recorded: Details show Healthy/Synced, main(c67aefd), Helm path and selected digest.
Collection date: (owner README). Current sync c67aefd; created timestamp is application metadata.
What this does not establish: GitOps sync revision is distinct from the artifact build revision. Argo health does not cryptographically authenticate the image.
Provenance and privacy review
Original capture reviewed and displayed unchanged. Any blacked-out source regions were already present in the original; this website added no edits. Review: .
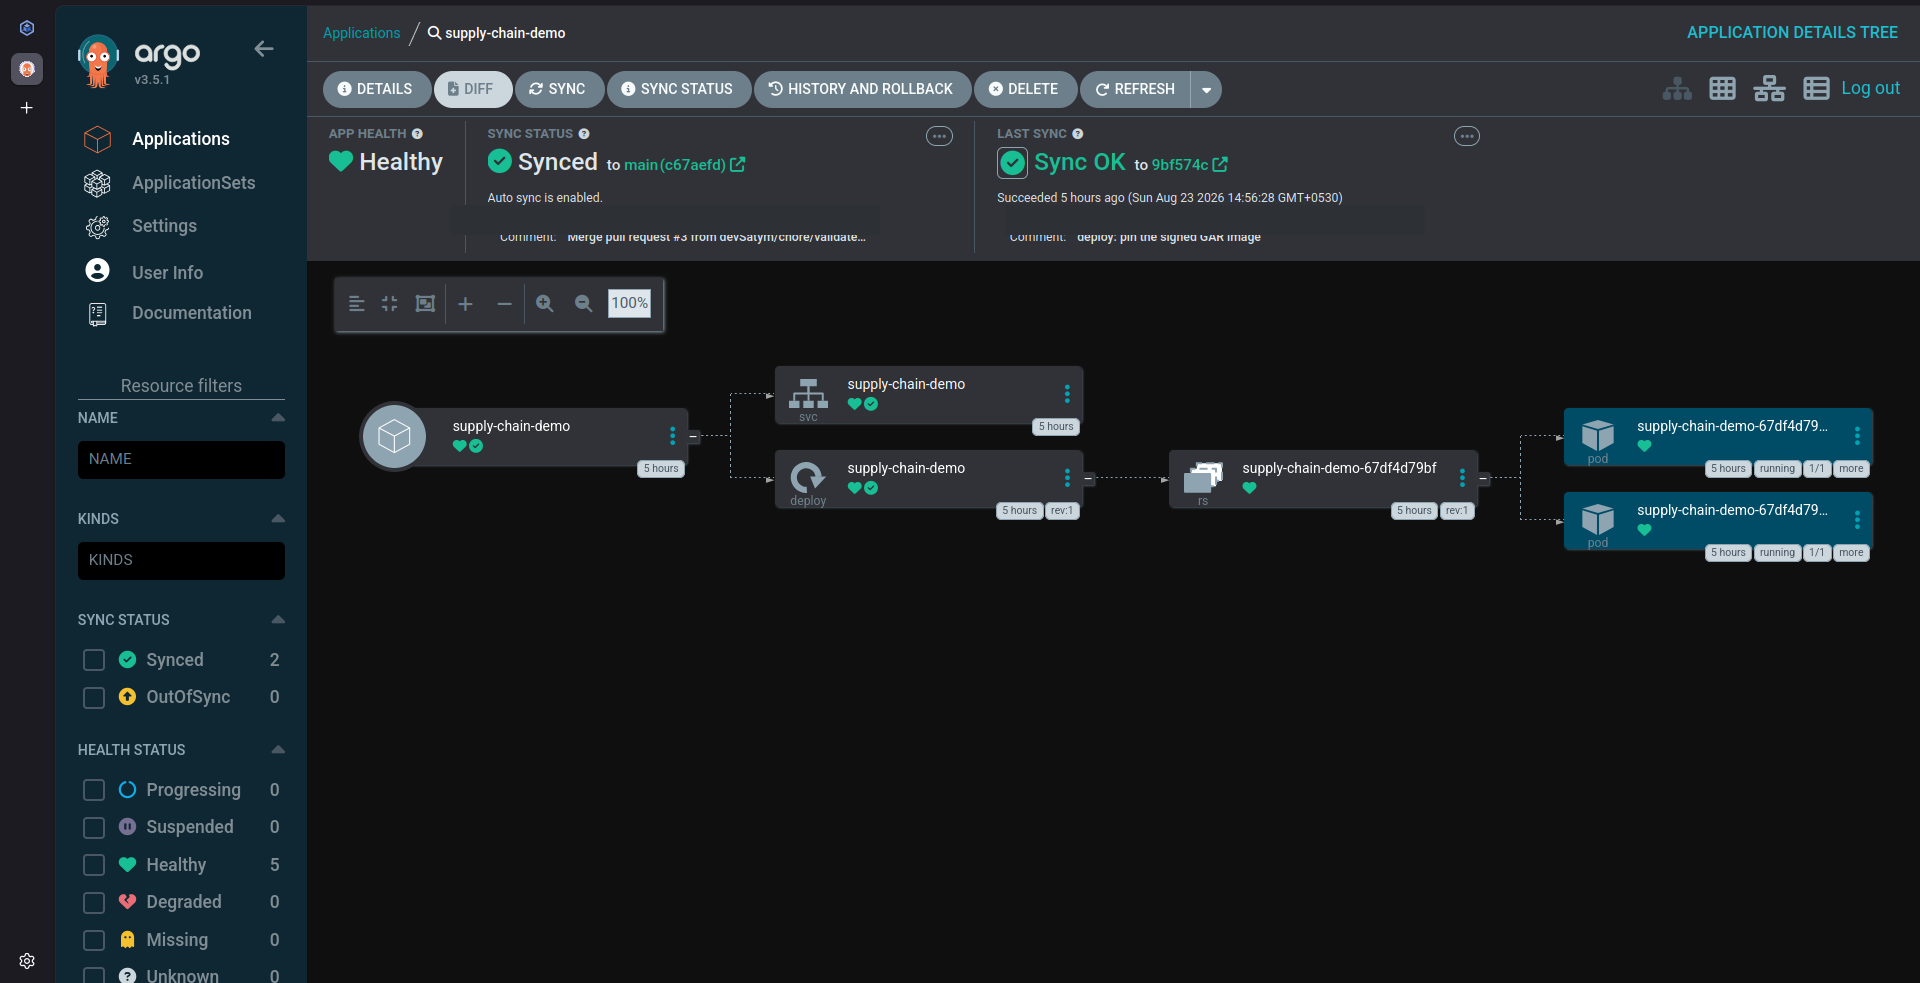
The application graph shows Healthy/Synced status with two running Pod nodes. Select the image to read the complete capture at full resolution.
Expected: Argo reports the reconciled application and its resources healthy. Recorded: Healthy/Synced and two Pod nodes are visible.
Collection date: (owner README). Current sync c67aefd; last successful sync 9bf574c is a separate field.
What this does not establish: This historical status does not prove current health, every policy decision or artifact build identity.
Provenance and privacy review
Original capture reviewed and displayed unchanged. Any blacked-out source regions were already present in the original; this website added no edits. Review: .
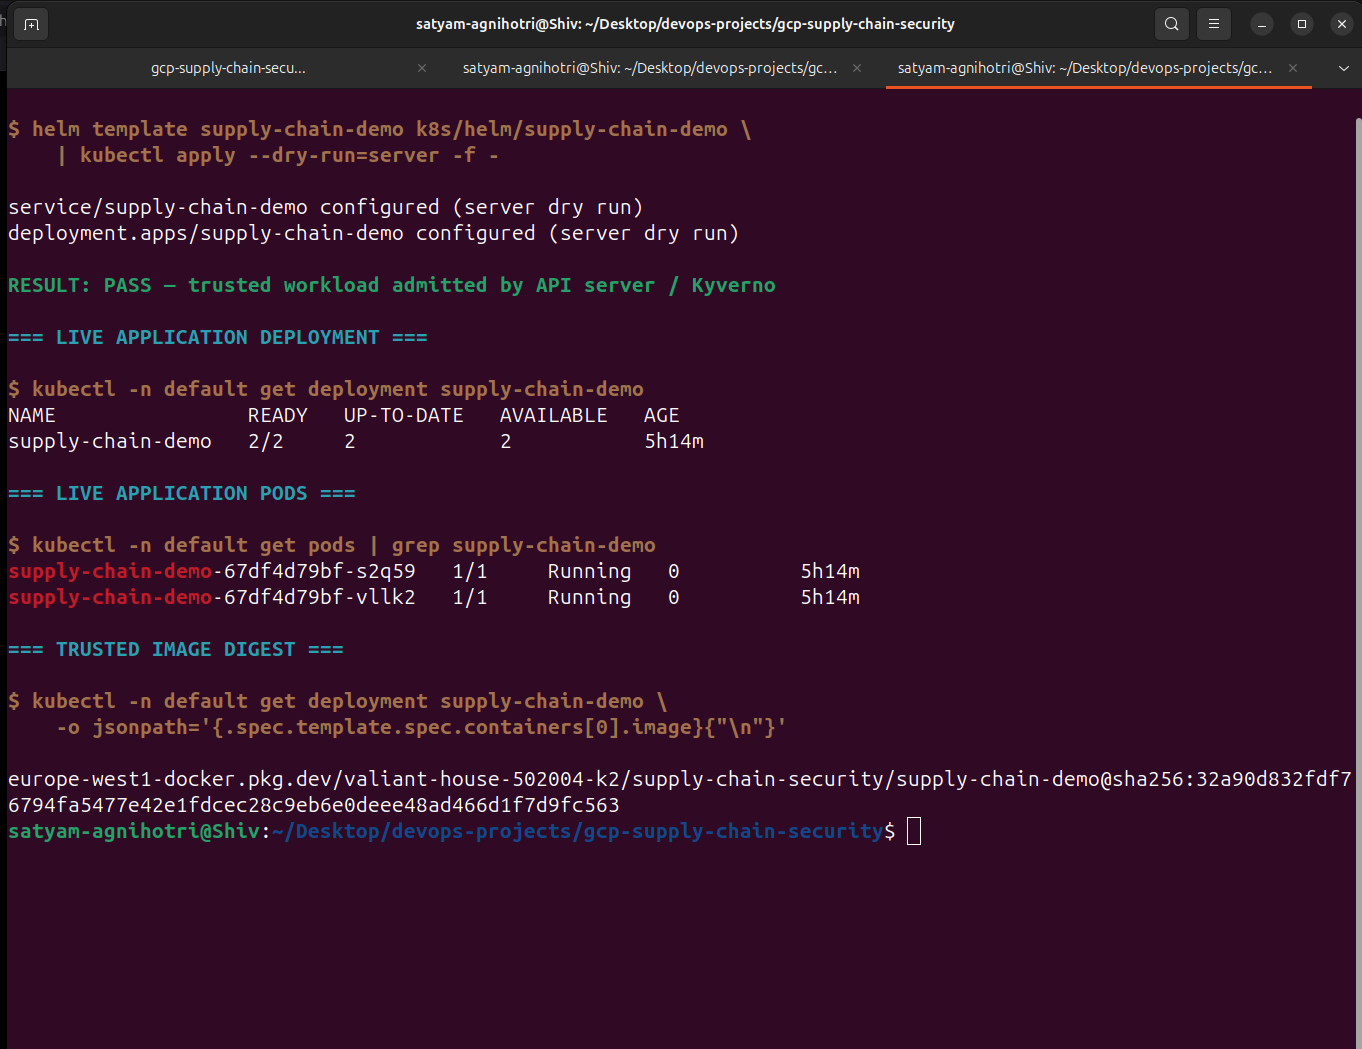
Trusted dry-run accepted; live replicas separately available
The signed release passes server dry-run; a separate query reports two available replicas. Select the image to read the complete capture at full resolution.
Expected: The matching trusted image is accepted under the configured admission policy. Recorded: Service/Deployment dry-run succeeds; a separate live query lists 2/2 replicas.
Collection date: (owner README). 32a90d artifact family; no installed policy revision is inferred.
What this does not establish: Dry-run does not create the separately listed replicas. Installed policy and artifact build revisions are not established by this image.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
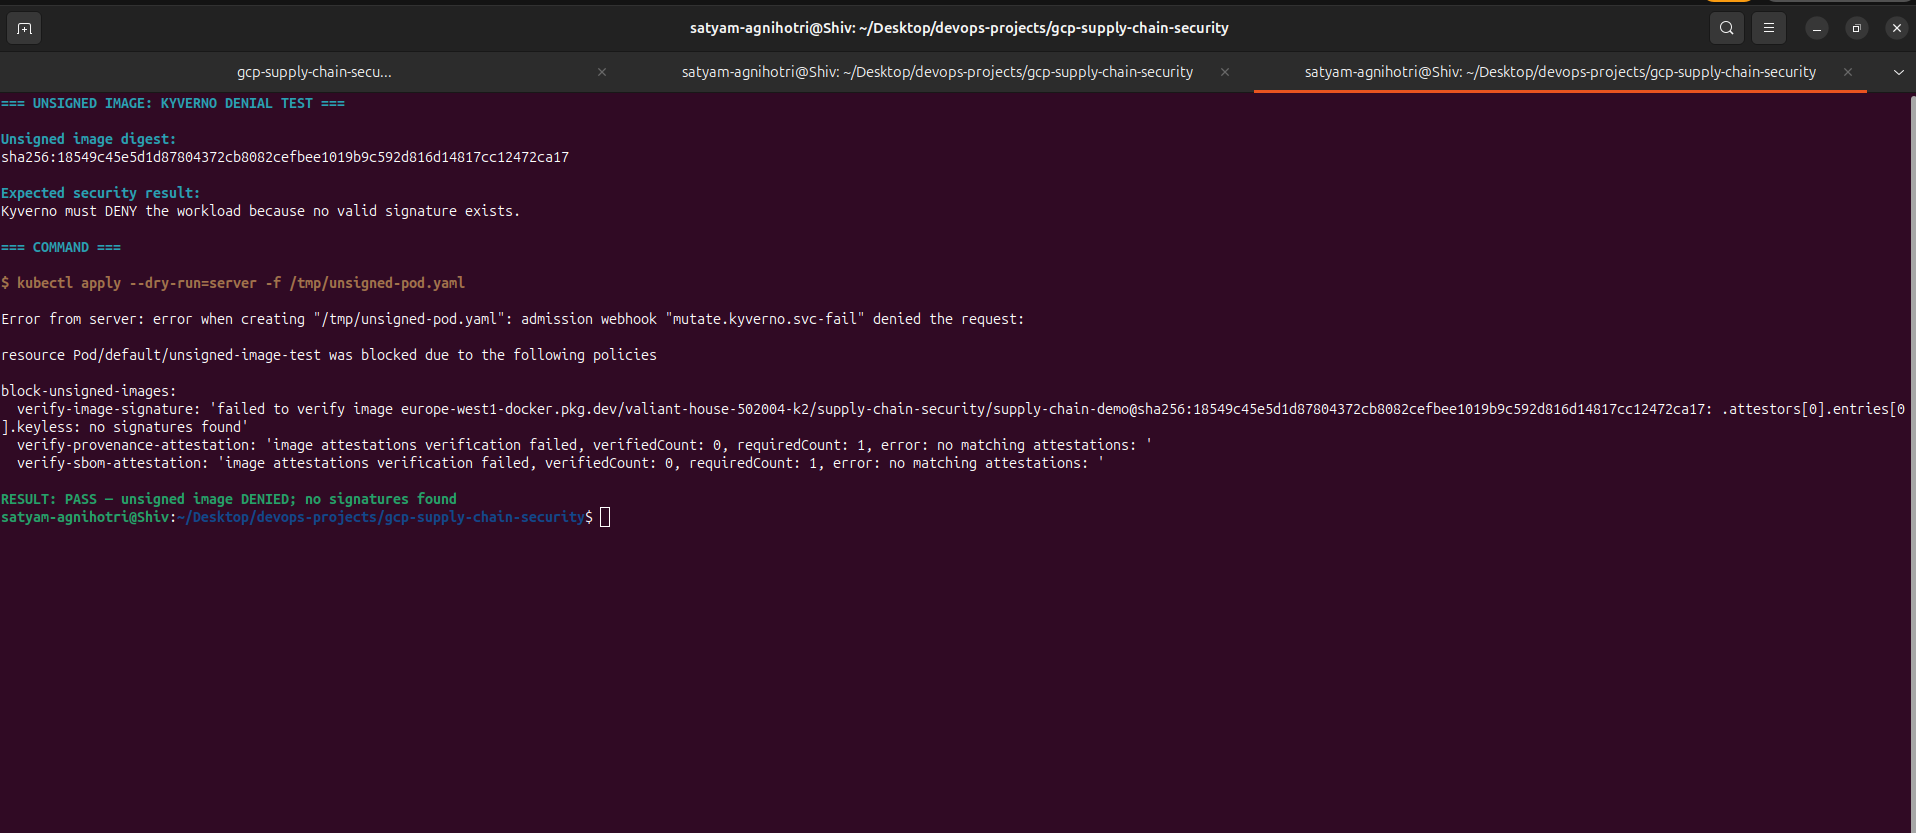
What this does not establish: Signature and both attestations are missing together. This is not an isolated requirement, excluded-namespace or unmatched-registry test.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
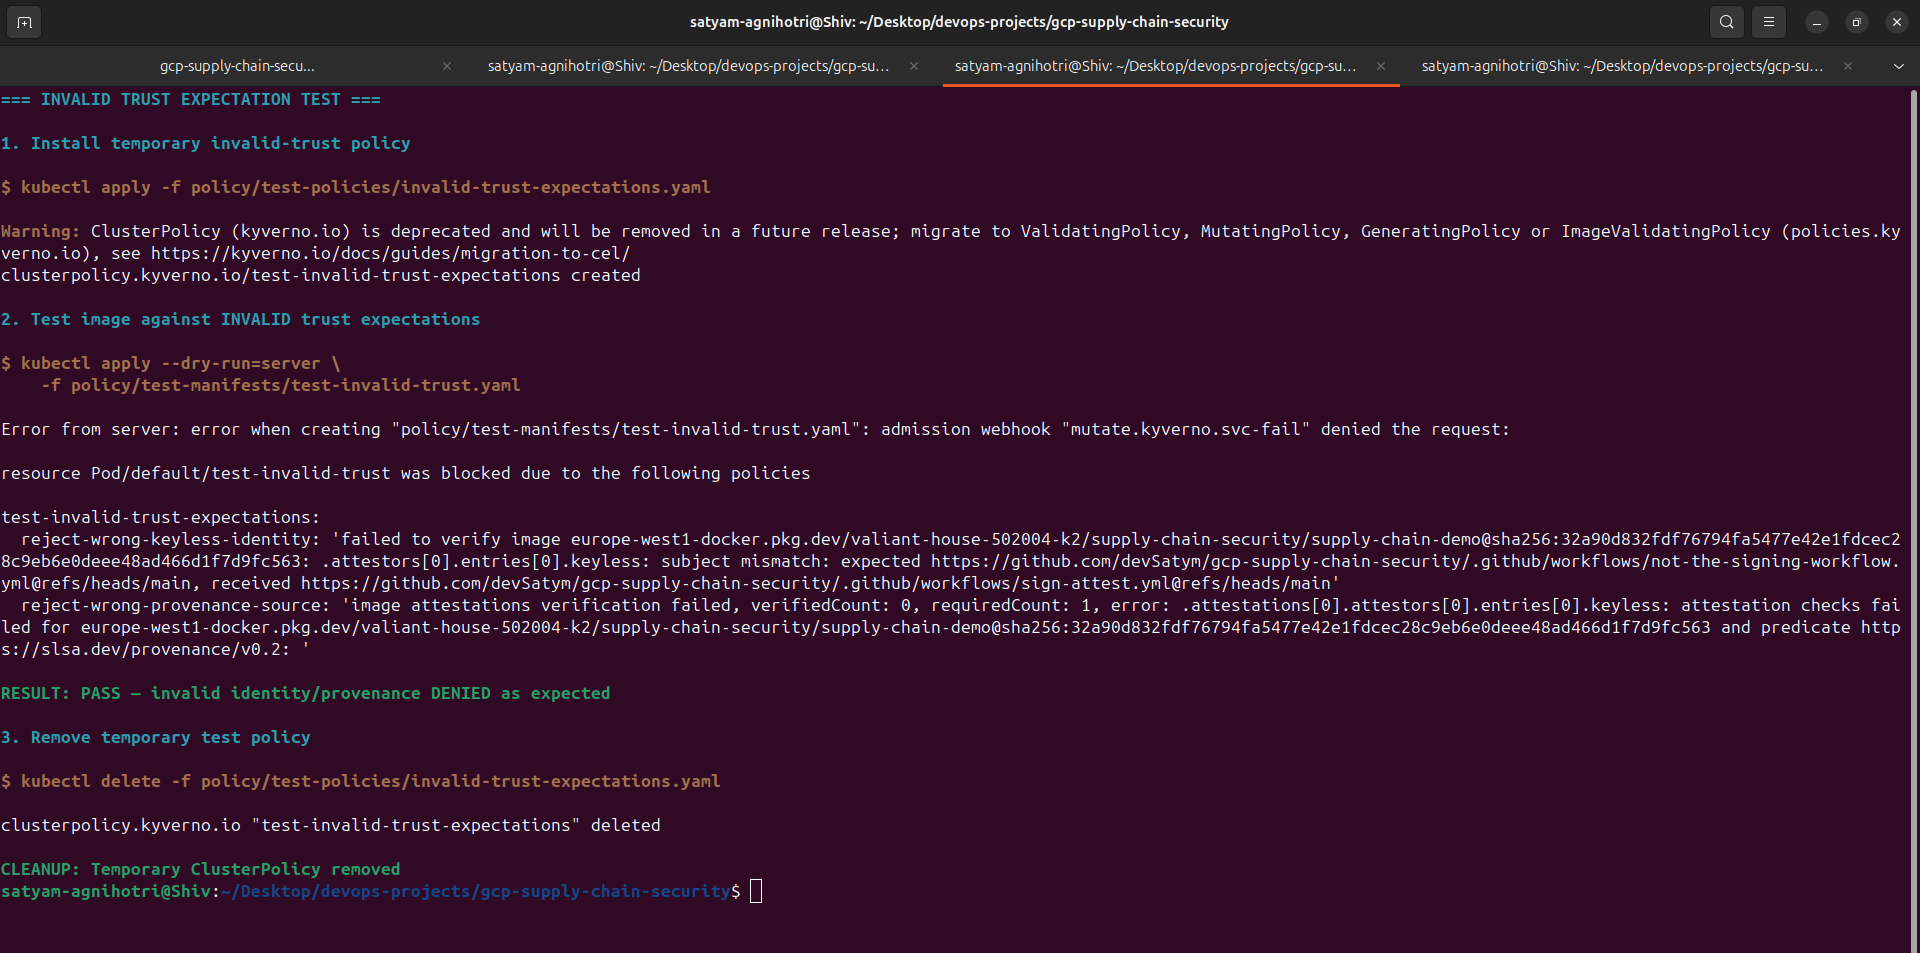
A temporary policy with changed signer/source expectations rejects a known signed digest and is then deleted. Select the image to read the complete capture at full resolution.
Expected: Reject signed claims that fail the configured trust expectations. Recorded: Denial details and subsequent temporary policy deletion are visible.
What this does not establish: Two expectations change together; the capture does not isolate which single condition would suffice or alter the signer/artifact.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
Both mixed-image fixtures containing an unsigned initContainer are denied. Select the image to read the complete capture at full resolution.
Expected: An approved regular image does not excuse an unsigned matched init image. Recorded: Both server dry-runs are denied with missing signatures/attestations.
Collection date: (owner README). Both reviewed fixtures use unsigned init containers.
What this does not establish: The fixture names do not demonstrate an unsigned regular sidecar or ephemeral-container path.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
The controlled shell returns UID/GID 10001; Falco subsequently records a Critical shell event. Select the image to read the complete capture at full resolution.
Expected: Record unexpected shell execution under the configured Falco rule. Recorded: id output is followed by the named Critical event in Falco logs.
Collection date: (owner README). Captured tag metadata is not a manifest digest or verified build revision.
What this does not establish: Detection follows execution. The rule name does not verify signatures; notification delivery and the exact runtime digest remain unestablished.
Provenance and privacy review
Reviewed original capture approved for display at the owner’s explicit request for all screenshots and subsequent Cloudflare publication. Existing source redactions remain intact. Any incidental terminal or account metadata remains visible. No additional pixel redaction was selected or applied. Review: .
All source references are pinned to cbbc807c0c150e106affa89fbb1b9e8349005749. All fourteen displayed images retain their original bytes and dimensions, including any redactions already present in the source captures. Technical commands, digests, trust identities, and outcomes remain visible. Original terminal/account metadata is also visible where present. The owner explicitly requested the complete collection and subsequently authorized Cloudflare publication with these approved originals. No additional pixel redaction was selected or applied. Any future derivative must be clearly labeled and carry its own displayed hash while preserving the source original.
The evidence catalogue supplies the detailed records and transcripts. Known gaps explains unverified paths and optional notification delivery. Local website image checks establish delivery and readability of the static assets, while remote publication, DNS, TLS, and current GCP execution remain separate states.