“ClusterPolicy” is a resource type, not evidence that every image in the cluster is verified. The baseline policy matches Pod requests in selected namespaces and verifies images under one registry path. Those qualifications determine its actual security boundary.
First evaluate image match and namespace exclusions.
Out of scope
Unmatched registry or excluded namespace: this rule supplies no assurance.
In scope
Require digest pin, signature, SBOM and selected provenance fields.
Allow
Required claims match the configured trust contract.
Deny
A missing claim or trust mismatch rejects the matching request.
Pod request → Out of scopeno scope match
Pod request → In scopescope matches
In scope → Allowclaims satisfy policy
In scope → Denymissing or mismatched claim
Enforce mode applies to matched images and namespaces; outage failurePolicy is a separate operational question.Text equivalent and limits
Unmatched image registries or excluded namespaces do not gain protection from this policy.
Matching Pod images must be digest pinned and have required signature and attestations.
Configured issuer, subject and selected provenance fields must satisfy the policy.
A trust mismatch denies a matching request; success permits admission, not permanent safety.
Read the labeled relationships as the stated contract. Optional connections are dashed and explicitly labeled; comparisons do not imply a sequential handoff. This figure explains inspected code or recorded observations, not current cloud execution.
Each of the three verification rules excludes namespaces whose kubernetes.io/metadata.name is kube-system, kyverno, argocd, crossplane-system, or cert-manager. The image reference pattern is the historical project’s europe-west1-docker.pkg.dev/.../supply-chain-security/* repository path. The explicit full path remains in the pinned implementation source.
Within that scope, the policy requires an approved keyless image signature, authenticated SPDX attestation, and authenticated SLSA v0.2 provenance satisfying builder, entrypoint, and source URI conditions. It configures mutateDigest: false, verifyDigest: true, and required: true in all three rules.
Images from unmatched registry paths are not covered by these verification entries. Excluded namespaces are not covered by these rules. There is no separate blanket rule in this file rejecting every image outside the application repository. A secure description therefore says “matching application images outside the listed exclusions”, not “all cluster workloads must be signed”.
The mixed fixture contains a signed regular container and an unsigned initContainer.Text equivalent and limits
The trusted acceptance capture establishes the signed regular-container path in its setup.
The unsigned-init fixture targets initContainers before application startup.
The mixed fixture combines signed application and unsigned init; it is not an unsigned regular sidecar experiment.
Ephemeral container subresource coverage remains unverified by these captures/tests.
Read the labeled relationships as the stated contract. Optional connections are dashed and explicitly labeled; comparisons do not imply a sequential handoff. This figure explains inspected code or recorded observations, not current cloud execution.
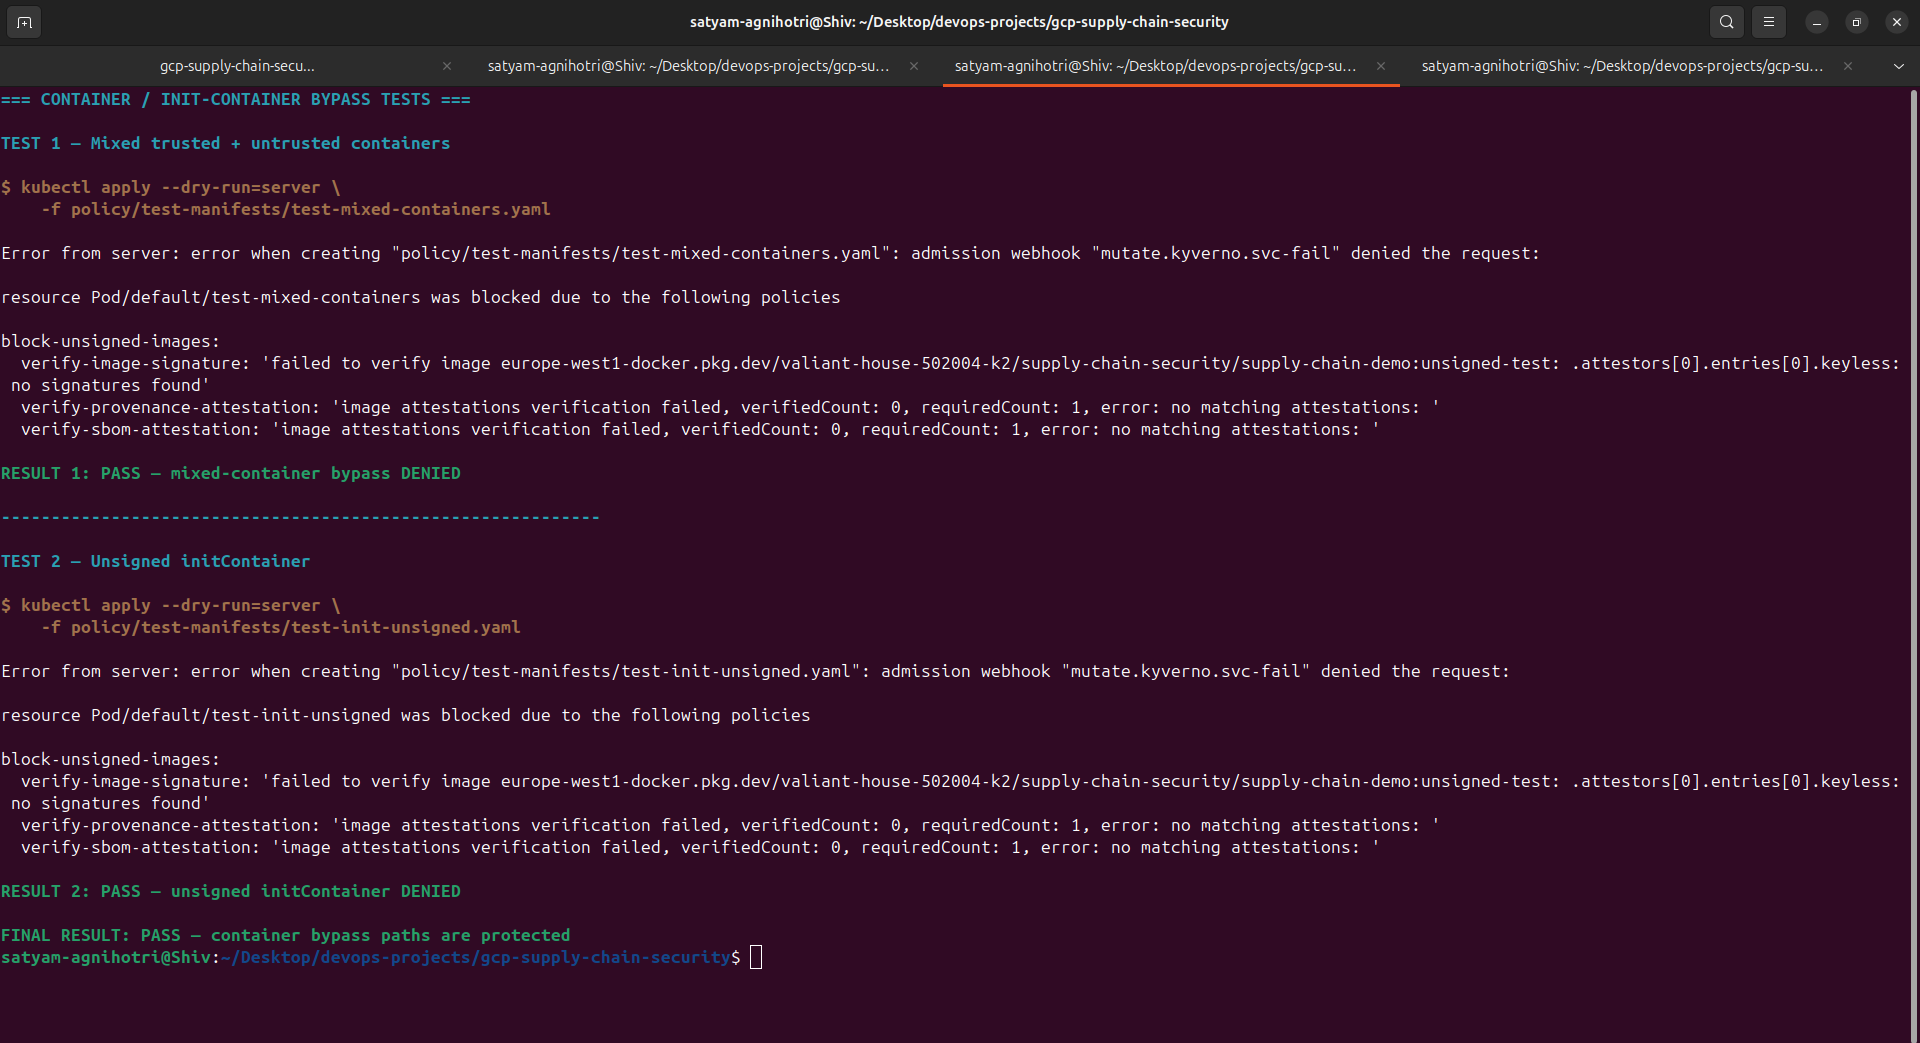
The baseline includes a signed regular-container fixture and two mixed-image fixtures. Both mixed fixtures contain a signed regular container plus an unsigned initContainer from the matching registry. The historical screenshot shows denial for both API-server dry-run requests.
This is strong evidence against that specific initContainer bypass. It is not separate proof for an unsigned regular sidecar beside a signed main container. No recorded ephemeral-container subresource test was found. Policy text and product capabilities are not substitutes for a tested installed-version path. The handbook therefore labels ephemeral-container coverage as unverified rather than inferring it from the policy title.
Both captured mixed-image fixtures with an unsigned initContainer were denied.
Recorded result: API-server dry runs for test-mixed-containers and test-init-unsigned were denied, each citing unsigned-test with no signatures and no matching attestations.
Both mixed-image fixtures containing an unsigned initContainer are denied. Select the image for full resolution.
Key limitation: The baseline YAML shows both fixtures use an unsigned initContainer alongside a signed regular container.
Transcript and provenance
Expected in this setup: An approved regular image must not excuse an unsigned matched init image in the same Pod.
Historical GCP, europe-west1; current environment not checked · observed 2026-08-23 · source revision unknown; not inferred from the documentation baseline
Selected visible output:
TEST 1 - Mixed trusted + untrusted containers
resource Pod/default/test-mixed-containers was blocked
verify-image-signature: supply-chain-demo:unsigned-test: no signatures found
verify-provenance-attestation: no matching attestations
verify-sbom-attestation: no matching attestations
RESULT 1: PASS - mixed-container bypass DENIED
TEST 2 - Unsigned initContainer
resource Pod/default/test-init-unsigned was blocked
verify-image-signature: supply-chain-demo:unsigned-test: no signatures found
RESULT 2: PASS - unsigned initContainer DENIED
Full limitations
The baseline YAML shows both fixtures use an unsigned initContainer alongside a signed regular container.
This does not establish unsigned regular sidecar or ephemeral-container subresource coverage.
The capture's final broad phrase about protected bypass paths is narrowed to the fields actually tested.
Visual review of original capture. Collection capture date attributed to docs/my-validation/README.md; this task did not rerun its cloud experiment. The original screenshot is approved for display at the owner’s explicit request for all evidence images and subsequent Cloudflare publication. Original terminal metadata remains visible. No additional pixel redaction was selected or applied. The selected transcript omits incidental prompts without changing the recorded result.
validationFailureAction: Enforce expresses rejection when a matching policy validation fails. A capture shows a webhook named mutate.kyverno.svc-fail denying the unsigned request. Neither detail alone specifies the complete API-server behavior when the admission controller is unreachable, times out, cannot authenticate to the registry, or cannot retrieve transparency data.
The committed Kyverno values file configures maximum context size and a Workload Identity annotation. It does not pin a Kyverno chart/controller version or include the installed webhook configuration. Those values do not establish a version-specific effective failure policy. No controller-outage or registry-outage experiment is claimed. Reproduction must inspect the effective webhook failurePolicy, timeout, namespace/object selection, controller version and policy error behavior before declaring a tested fail-closed availability contract.
A denial on an unsigned image demonstrates working rejection, while an outage tests whether necessary decisions remain available. Treating those as the same experiment would hide an operational trade-off: failing closed can prevent an unsafe request and can also block recovery or legitimate deployment during a verifier incident.
The policy sets background: true. That configuration should not be read as automatic removal of already running workloads. Background policy reporting and admission decisions are different execution paths. The supplied evidence does not demonstrate retroactive eviction, continuous cryptographic revalidation, or automatic termination after metadata disappears.
The repository preserves earlier Gatekeeper/Ratify configurations and historical evidence. Their namespace lists, identity trade-offs, and webhook behavior must not be silently assigned to the active Kyverno acceptance path. The GCP edition explains the source and captures that actually support each claim.
Namespace exclusions can reduce conflicts with system controllers, while leaving privileged infrastructure outside this artifact-origin contract. A narrower registry scope limits operational impact, while leaving unmatched image sources unverified by these entries. Availability behavior can favor rejection during uncertainty, while making controller recovery harder. These are design responsibilities to examine explicitly, not bypass instructions.